This guide explains Doe Ess in an evidence-minded way, covering what it typically refers to, how stakeholders evaluate it, and what to consider before choosing a provider or approach. Objectively, the term is commonly used as a shorthand identifier across discussions, so buyers should verify scope, outputs, and support terms in writing. The article then adds decision conditions, requirements, and FAQs.
When people reference Doe Ess, they often mean a specific product/service identity, process label, internal shorthand used in planning and procurement, or a compact name attached to a bundle of capabilities. Because the same phrasing can be used differently across industries, organizations, contracts, and vendors, the most important step is not to assume a universal definition. Instead, treat Doe Ess as a “needs-to-be-verified” term: confirm what is included, what success looks like, what artifacts or documentation support the claim, and what is explicitly excluded.
From an industry-expert perspective, the evaluation of anything branded or labeled with a short identifier like Doe Ess should follow a structured due-diligence workflow. You want clarity on scope, deliverables, timeline, responsibility boundaries, quality checks, and change-management rules. This is especially important when you may be comparing multiple suppliers, systems, or service bundles that appear similar at first glance because they share the same shorthand label.
In practice, the difference between a good procurement decision and a problematic one often comes down to whether the buyer verifies meaning through documentation and acceptance criteria, rather than relying on a label. A label may be stable internally, but externally—across different companies, consultants, and even different teams within the same organization—meaning can shift. Two parties can both say “Doe Ess” and still be talking about different things: different features, different performance levels, different installation methods, different support commitments, different timelines, different data handling assumptions, different compliance obligations, or different levels of effort.
Verification matters because it reduces ambiguity and makes outcomes measurable. It also helps establish accountability if things go wrong. If you have a written definition, written acceptance criteria, written responsibility boundaries, and an agreed mechanism for change requests, then disputes are easier to resolve and improvements are easier to plan. If you do not have these elements, you can end up with rework, delays, cost overruns, inconsistent deliverables, or confusion about who is responsible for fixing defects.
Short identifiers—such as Doe Ess—often emerge for practical reasons. Teams need quick reference codes during planning. Procurement categories need consistent labels. Technical communities use compact shorthand for repeatable configurations. Vendors market offerings using memorable acronyms or phrases. In internal documents, short identifiers improve readability and allow stakeholders to refer to complex bundles without writing lengthy descriptions each time.
The downside is that meaning can drift. The same label might be reused for convenience, might evolve across version releases, or might be applied differently by different vendors. Even when the label was originally created by one organization, other organizations may reinterpret it—intentionally or unintentionally. Over time, a label can become a “container” that appears to hold everything relevant, while in reality it might hold only a portion of what stakeholders assume.
Accordingly, any objective buyer or analyst should separate three layers:
If you evaluate Doe Ess only at the “label” layer, you risk mismatch. If you evaluate it across all three layers, you reduce ambiguity and avoid scope creep. Put simply: the label tells you what to ask about; it does not tell you what you are buying.
Another common source of misunderstanding is the assumption that a label is stable across time. Many offerings change: pricing models update, underlying systems upgrade, processes become more refined, and support models adjust based on lessons learned. Vendors may keep the same label while modifying the details underneath. Therefore, verification should include not only “what does Doe Ess mean today,” but also “what will change during implementation and after go-live,” including versioning and release policies.
Finally, terms like Doe Ess can have different meanings across stakeholder groups. Engineering might interpret the label as a technical configuration. Operations might interpret it as a managed service with specific uptime and response times. Procurement might interpret it as a purchased item with defined deliverables and acceptance steps. Legal might interpret it as a contract scope with remedies and limitation-of-liability clauses. Because these interpretations differ, the buyer needs a cross-functional alignment process to make sure everyone is operating on the same “real definition.”
Industry practitioners typically treat procurement decisions like risk-managed selections. Rather than trusting labels, they verify scope and capabilities through structured questions, formal documentation requests, and measurable acceptance criteria. Here is a method that aligns with standard purchasing and quality management thinking (including widely used vendor management practices, where documentation and verification are central). The framework is designed to be domain-agnostic: it works whether Doe Ess refers to an installation package, a managed service, a software-related service bundle, a consulting engagement, a compliance process, a logistics workflow, or any other product/service identity that is summarized by a short label.
Before applying the framework, it helps to adopt a mindset: every ambiguous phrase is a risk, and every risk should be converted into a question with a documented answer. If the supplier cannot answer the question in writing—or cannot attach an artifact that proves their answer—then the buyer should either clarify, renegotiate, or pause.
For Doe Ess, request a plain-language scope statement and a list of deliverables. The goal is to make the offering tangible. Deliverables should be described in a way that a non-expert can understand what will be produced, delivered, installed, configured, or performed. If the vendor cannot clearly enumerate items, the buyer should treat that as a signal to slow down.
To make scope evaluation concrete, consider requiring the supplier to provide:
One practical approach is to ask the supplier to fill in a “deliverables grid.” Each line includes: deliverable name, format, due date or milestone, acceptance criteria, and the party responsible for sign-off. If the supplier cannot produce this grid, you will likely encounter issues where work is performed inconsistently or where acceptance becomes subjective.
Also pay attention to whether Doe Ess is delivered as a one-time outcome or as an ongoing capability. Some labels describe a project deliverable; others describe a managed relationship. The scope and deliverables differ significantly between a fixed deliverable package and an ongoing service.
Finally, clarify whether deliverables are “best effort” or “committed.” The buyer wants to know whether outcomes are guaranteed to meet certain performance thresholds, or whether the supplier merely commits to performing steps without guaranteeing results. This distinction should be spelled out in writing.
Even when stakeholders agree on the label (Doe Ess), they may disagree on quality. Require measurable acceptance criteria, such as inspection checkpoints, performance thresholds, documentation quality standards, testing protocols, and sign-off procedures. Acceptance criteria should be specific enough that both parties can check compliance without debate over subjective interpretations.
Effective acceptance criteria usually include at least three elements:
In many engagements, acceptance criteria are not just about technical correctness. They also cover:
When acceptance is poorly defined, disputes multiply. For example, a supplier might say a deliverable is “done” because it was delivered, while the buyer expects it to meet a specific performance requirement. The acceptance criteria should prevent this by stating what must be true at acceptance time.
Also require the supplier to define “rework” and “remediation” pathways. If something fails acceptance, what happens next? Who fixes it? How long does it take? Does the original timeline shift? Are there repeat testing costs? A well-defined acceptance and remediation model reduces friction and protects both sides.
An industry-quality approach clarifies responsibilities across parties. When you evaluate Doe Ess, ensure you understand escalation paths, turnaround times, ownership of defects, handling of incidents, and how revisions are handled if results are not acceptable.
Responsibility boundaries are especially important because many “labels” cover multiple activities that span different teams and systems. Without clarity, issues can bounce between parties, causing delays. A responsibility boundary discussion should include:
In practical terms, you can require a RACI-style mapping (Responsible, Accountable, Consulted, Informed). This mapping should cover key lifecycle moments: discovery, implementation, testing, acceptance, go-live, stabilization, and ongoing support.
Also clarify what constitutes a supplier “failure” versus a buyer “input” issue. Many outcomes depend on buyer-provided inputs: access credentials, requirements documentation, data readiness, change approvals, or internal scheduling. The supplier should specify which inputs are required and what happens if they are missing or delayed. Conversely, the buyer should not assume that any problem is automatically the supplier’s fault if critical inputs were not provided in time.
Finally, boundary clarity helps with compliance and auditability. If an issue triggers a compliance requirement (for example, security incident reporting or data handling violations), responsibility must be clearly assigned so that regulatory deadlines are met.
For anything associated with Doe Ess, insist on verifiable materials. Documentation might include specifications, test results, quality checklists, standard operating procedures, change logs, runbooks, audit reports, security documentation, and written policies. The purpose is twofold: (1) verify that what is promised can be delivered, and (2) ensure you can operate and maintain what you receive.
Documentation is also essential for operational continuity. Even if the supplier performs well at the start, the buyer needs continuity artifacts: how to run the process, how to monitor it, how to escalate issues, how to apply updates, and how to troubleshoot. If documentation is thin, the buyer becomes dependent on the supplier for routine tasks.
When documentation is requested, pay attention to three qualities:
One useful practice is to ask for “sample artifacts” that correspond to the delivered outputs. For example, if deliverables include reports, ask for a redacted sample report. If deliverables include SOPs, ask for sample SOPs. If deliverables include testing evidence, ask for test summaries. Sample artifacts reduce reliance on promises and allow the buyer to evaluate real quality.
Also consider audit readiness. In many industries, buyers must prove compliance after the fact. If the supplier cannot provide documentation that supports compliance audits, the buyer may be forced into costly remediation or may face compliance risk.
Even without publicly provided price details in your prompt, decision-making should still consider total cost of ownership (TCO). TCO includes onboarding effort, recurring maintenance, rework costs, operational overhead, and any compliance-related costs that may arise after selection.
Many buyers mistakenly focus only on the initial contract value. But with services and ongoing systems, the bigger cost driver can be operational friction: training time, internal staff involvement, recurring support, replacement cycles, and the cost of handling issues. When Doe Ess is a managed service or process, it’s especially important to estimate long-term costs.
TCO evaluation often includes:
A buyer should also ask how costs scale. If Doe Ess pricing scales with volume, usage, number of incidents, or number of users, then the buyer must understand usage patterns and expected growth. Without this, you might sign a deal that appears affordable upfront but becomes expensive later.
Finally, evaluate “cost-to-quality.” Cheaper offerings sometimes require more buyer involvement or more internal remediation work. The TCO view should help you see beyond sticker price and toward overall operational efficiency.
In supply-chain and service environments, a “supplier” is not only the provider of the primary deliverable; it is also the provider of continuity—support, replacements, versioning, update management, issue response, and operational stability. When comparing suppliers for something referred to as Doe Ess, focus on operational maturity and how reliably they can deliver to the same standard over time.
When evaluating supplier readiness, buyers often examine:
One frequent pitfall is evaluating only the “sales story.” A supplier may present impressive capabilities during a proposal but may not have the delivery capacity to meet commitments once the contract is signed. Therefore, ask about how delivery is executed: project management practices, quality gates, and how escalations are handled internally.
It is also helpful to evaluate the supplier’s tooling and methods. For example, do they use standardized ticketing for support? Do they keep change logs? Do they perform root-cause analysis for recurring issues? Do they have formal procedures for incident communication? These details reveal whether the supplier can operate reliably when something goes wrong.
Finally, consider supplier stability. Vendors that change leadership frequently, reorganize their service model often, or show signs of operational instability can increase delivery risk. While the label Doe Ess may be stable, supplier capability might shift, affecting performance and support quality.
Your request includes placeholders for price information and supplier details, but no specific figures were provided. In such cases, an objective approach is to structure pricing discussions without fabricating numbers. The correct goal is to align cost categories with scope, deliverables, and acceptance criteria.
Practically, ask suppliers to quote using a consistent breakdown for Doe Ess, such as:
If a supplier cannot align pricing with scope and acceptance criteria, the buyer should treat that as a risk. Poor cost alignment often signals that the supplier is not thinking about deliverables and verification in a disciplined way, increasing the likelihood of disputes over additional work.
A responsible pricing conversation also addresses how the supplier handles uncertainty. For example, if implementation depends on unknowns (data quality, infrastructure readiness, or internal approvals), then suppliers might propose contingencies. Buyers should require contingencies to be documented clearly: what assumptions are being made, what triggers the contingency, and how it is approved.
When comparing multiple suppliers, ensure you compare apples to apples. A supplier may quote a lower price for Doe Ess but include fewer deliverables, weaker acceptance criteria, fewer support hours, or limited documentation. Conversely, a higher priced option may include stronger verification evidence, clearer escalation mechanisms, and better change control. Price is meaningful only when normalized to scope and quality expectations.
Finally, consider contract structure: fixed price vs time-and-materials vs hybrid structures. The contract type influences risk allocation. A fixed price can reduce cost uncertainty for the buyer but may shift risks to the supplier, sometimes leading to tighter scope boundaries or more change orders. Time-and-materials may provide flexibility but can increase cost risk unless controls are strong. The best approach depends on how well requirements are defined and how stable the environment is.
Your instruction includes replacing city/country placeholders with “nearby.” Since no explicit location appears in the supplied keywords, the guidance stays generally applicable. In practice, however, localization influences operational details even if the core scope is the same. Local expectations can affect onboarding speed, communication norms, scheduling cycles, availability of resources, and how quickly issues can be resolved.
Consider that “nearby” can mean different practical things in different industries:
Many buyers in regions with strong small-business ecosystems prefer clear communication norms: phone-and-email workflows, predictable response windows, and structured follow-up. Even if Doe Ess is delivered remotely, early onboarding success can depend on whether the supplier communicates effectively with the buyer’s stakeholders.
Therefore, you should not treat “nearby” as a vague marketing phrase. Instead, confirm what “nearby” means in the operational plan. For example, ask whether onsite visits are included, how quickly onsite support can be scheduled if required, and whether the supplier has local partner capacity for replacements or specialized tasks.
Localization also impacts training and adoption. If end users prefer local language documentation, or if training must be delivered in specific formats, you should confirm these requirements. If not confirmed, they may become sources of friction during implementation.
Below is a supplement-style comparison table to support decisions around Doe Ess. It is intentionally generic because your prompt did not provide domain-specific attributes, prices, or supplier names. Still, it is useful as a template to structure vendor evaluation and to ensure that the buyer verifies meaning beyond the label.
| Evaluation Area | Good Practice for “Doe Ess” | What to Verify in Writing | Typical Requirement |
|---|---|---|---|
| Definition | Clear scope statement tied to the label “Doe Ess” | Exact description, boundaries, and included components | One-page scope summary + referenced standards |
| Deliverables | Enumerated outputs with acceptance criteria | Deliverable list, format, quality checks, sign-off process | Checklist-based acceptance |
| Timeline | Realistic schedule with dependencies | Milestones, lead times, and revision windows | Implementation plan and start date conditions |
| Supplier capability | Demonstrated ability to deliver similar work | Case summaries, references, or proof of comparable capability | Documented track record |
| Support and escalation | Defined response and escalation path | Support hours, severity levels, turnaround expectations | Support policy and incident workflow |
| Cost transparency | Pricing linked to scope and change control | Cost breakdown, what triggers additional charges | Quoted cost schedule + change-order rules |
| Quality assurance | Repeatable QA process | Test/inspection methods and documentation format | QA plan + audit artifacts |
| Data and compliance | Defined handling, privacy, and compliance approach | Data retention, access controls, and compliance commitments | Data handling policy and responsibility matrix |
| Change control | Clear rules for revisions and scope changes | Change request workflow, approval authority, pricing method | Change order procedure with documented SLAs |
| Knowledge transfer | Documentation and handover for continuity | Runbooks, training materials, handover schedule | Handover checklist + training sign-off |
To use the table effectively, do not merely “check a box.” Instead, require evidence. For every item you mark as good practice, request at least one artifact that shows how the supplier meets that practice. The “verification” goal is to convert evaluation into proof.
This section provides a structured, step-by-step guide you can apply regardless of the domain in which Doe Ess is used. The aim is to reduce ambiguity and increase decision quality, especially when you are comparing suppliers or negotiating scope and cost.
Even if you do not have complex procurement processes internally, you can still use these steps as a lightweight due-diligence checklist. The value comes from asking consistent questions and getting consistent documentation responses.
Ask the supplier or internal stakeholders to define Doe Ess in a short paragraph and then provide a scope document. If multiple interpretations exist, you need to resolve them early. A useful tactic is to require the supplier to produce both a “plain-English definition” and a “formal scope” version. The plain-English version helps alignment; the formal scope version helps enforceability.
Also confirm whether Doe Ess is a stable offering or a versioned product/service. If it’s versioned, ask which version is being proposed, what changes are included compared to prior versions, and how versions are updated.
Ask for deliverables, acceptance criteria, and QA artifacts. For example, “How will you measure success for Doe Ess?” should have a direct answer with measurable criteria. Request the acceptance pack as a single coherent document, not scattered snippets. This helps you verify completeness and consistency.
The acceptance pack should include:
Hold a meeting that includes the buyer, end users, and the supplier. Confirm who does what, when, and how sign-off will happen. This meeting should also address assumptions and dependencies. For example, if the supplier’s work depends on buyer-provided access or data, that should be stated explicitly.
To reduce ambiguity, it can help to end the meeting with a written “open questions list” and “decisions log.” Decisions should be recorded with owners and due dates. Any unresolved items should become explicit risks with a mitigation plan.
Request a price proposal that maps to scope. Even if you are not given exact numbers here, insist on cost categories that match the deliverables and timelines. The key is traceability: each cost line should connect to a deliverable or service element.
When reviewing the quotation, look for:
Request documentation that demonstrates consistent delivery. This may include process descriptions, sample reports, sample checklists, test results, or quality gate descriptions. Ask how they handle recurring issues and how they prevent defects from repeating.
Evidence can also include:
Agree on what constitutes a change request, how it is priced, and how it affects timelines. This is essential for preventing unplanned expansions of the Doe Ess scope. Without change control, ambiguity becomes expensive.
A strong change control plan specifies:
If your domain allows it, use a staged approach. A controlled initial phase reveals integration challenges and clarifies performance expectations. Staging also helps confirm that acceptance criteria can be met in real conditions, not just in proposal documents.
For staged rollouts, define what “success” means for each phase. For example, Phase 1 might focus on operational readiness and baseline performance, while Phase 2 might focus on scaling or expanding features.
Make sure your team receives the knowledge needed for continuity: documentation, operational steps, and the escalation path for issues. Confirm who will be available during go-live and stabilization periods, and what happens if issues persist beyond agreed resolution windows.
Handover should include:
Keep records of scope definitions, acceptance criteria, pricing breakdowns, and approvals. This is the foundation of accountability for Doe Ess outcomes. Your sign-off records should be accessible to stakeholders who may need them later—such as internal auditors, compliance reviewers, operations staff, or legal teams.
In many organizations, these records also become important when you renew contracts or expand scope, because they establish baseline definitions and acceptance thresholds.
Not all situations are ready for immediate procurement. Consider pausing or re-negotiating if you observe any of the following around Doe Ess:
When these issues appear, the appropriate response is usually not to abandon the idea immediately, but to renegotiate terms to convert ambiguity into written commitments. Sometimes the supplier can revise their proposal quickly once they understand what you need for verification.
However, there are cases where pausing is the best choice because renegotiation becomes repetitive. If a supplier repeatedly provides vague answers or refuses to provide evidence, then the risk may be structural. In that situation, you may be better off choosing a different supplier or redefining the project in a smaller, more testable form.
It may be used as a shorthand label, but your objective approach should treat it as context-dependent. Confirm what the term means in your specific industry and with the specific supplier or internal team. Even if one organization uses the label consistently, other organizations may use it differently.
Ask for a written definition tied to scope, a deliverables list, acceptance criteria, QA evidence, and a structured quotation that maps cost to those deliverables. Also ask what is excluded and what assumptions the supplier is making, because exclusions and assumptions often matter as much as inclusions.
You can compare them, but only after normalizing scope and acceptance criteria. Two suppliers may use the same label while delivering different capabilities, different performance levels, different documentation quality, different support coverage, or different change control policies. A label match is not a contract match.
To compare fairly, require both suppliers to provide a scope-and-acceptance pack using the same evaluation structure. Then compare deliverables, acceptance evidence, support models, and change control rules. Only after normalization should you consider price.
Use a scope-and-acceptance pack, define revision boundaries, and require a change-order process. Ensure the pricing proposal is aligned with deliverables and milestones. In addition, confirm how disputes are handled and whether the supplier must continue work while changes are approved (and under what conditions).
Another protective measure is to include measurable milestones tied to acceptance. If payments are linked to completion of defined deliverables, it becomes easier to prevent cost drift and to hold both sides accountable to the plan.
Credible evidence typically includes documented processes, test/inspection summaries, sample outputs, sample reports, and consistency indicators (e.g., repeatable QA). Avoid relying on claims without documentation. Even strong verbal assurances can be unreliable if the supplier cannot provide artifacts.
Credibility also improves when evidence includes traceability: e.g., test evidence that corresponds to specific acceptance criteria. Ask for evidence that maps to the criteria, not evidence that is merely “related.”
No. The guide is written to be domain-agnostic. Because “Doe Ess” can be used in multiple contexts, you should map the steps and conditions to the actual definition used in your case. If you tell me what Doe Ess refers to in your scenario—product type, service type, operational process, or domain—I can tailor the evaluation questions, acceptance checkpoints, and supplier comparison criteria more precisely.
Because your prompt did not specify a domain for Doe Ess, the guidance is based on widely accepted procurement and quality-management principles rather than domain-specific statistics or unverified performance claims. For reliability, readers can consult official or widely recognized standards and research such as:
Even without citing a specific statistic, the core message remains: quality and procurement decisions work best when they are measurable, documented, and verifiable. That is precisely what the framework above aims to enforce for Doe Ess.
If you share the actual context of Doe Ess (e.g., product category, service type, operational process, compliance requirements, or deliverable outcomes), you can often translate these general principles into very specific acceptance metrics and verification artifacts that match your domain.
The central lesson is straightforward: Doe Ess should be treated as a starting identifier, not a complete description. By requiring a verified scope, explicit acceptance criteria, transparent cost mapping, and documented supplier capability, you move from guesswork to a defensible decision process.
Whether you are evaluating one supplier or comparing several “nearby” options, the same discipline applies: define it, verify it, and document it. When Doe Ess becomes a defined outcome—supported by evidence and measurable acceptance—you protect your organization from ambiguity, reduce the risk of scope drift, and create a clear accountability structure for success.
In other words, the right outcome is not simply “we bought Doe Ess.” The right outcome is “we bought the documented set of deliverables and performance expectations that were verified before commitment, and we accepted work against measurable criteria after verification.” That is what turns a label into a reliable purchase.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
4rkojvsx Technology: Industry Insights and Buying Guide
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
A Practical Guide to Londonderry Towers
Londonderry Towers is discussed here as a residential building concept—useful for understanding what buyers and renters typically evaluate. Objectively, “Londonderry” is associated with Northern Ireland and the city region, while “Towers” signals a multi-storey living development. This guide focuses on how stakeholders assess location, building features, costs, and supplier credibility, with conditions and requirements provided later.
Ade Sara Guide: Supplier, Pricing, and Choosing Wisely
Ade Sara plays a central role in many product discussions, especially when buyers compare supplier reliability, pricing structure, and intended use. This guide provides objective background on the keyword, outlines how to evaluate quotes without relying on marketing claims, and explains practical requirements for sourcing decisions that remain consistent across suppliers.
Reliable Service Support Through 07915491784
This guide explains how to use 07915491784 for practical, reliable service support and enquiries while comparing supplier approaches and handling requirements. Objectively, phone-based contact systems connect customers to service teams, improve response tracking, and support consistent documentation—especially when questions involve pricing, availability, and process steps. Use the sections below to evaluate providers carefully.
Understanding Gac Jordan: Selection, Pricing, and Sourcing
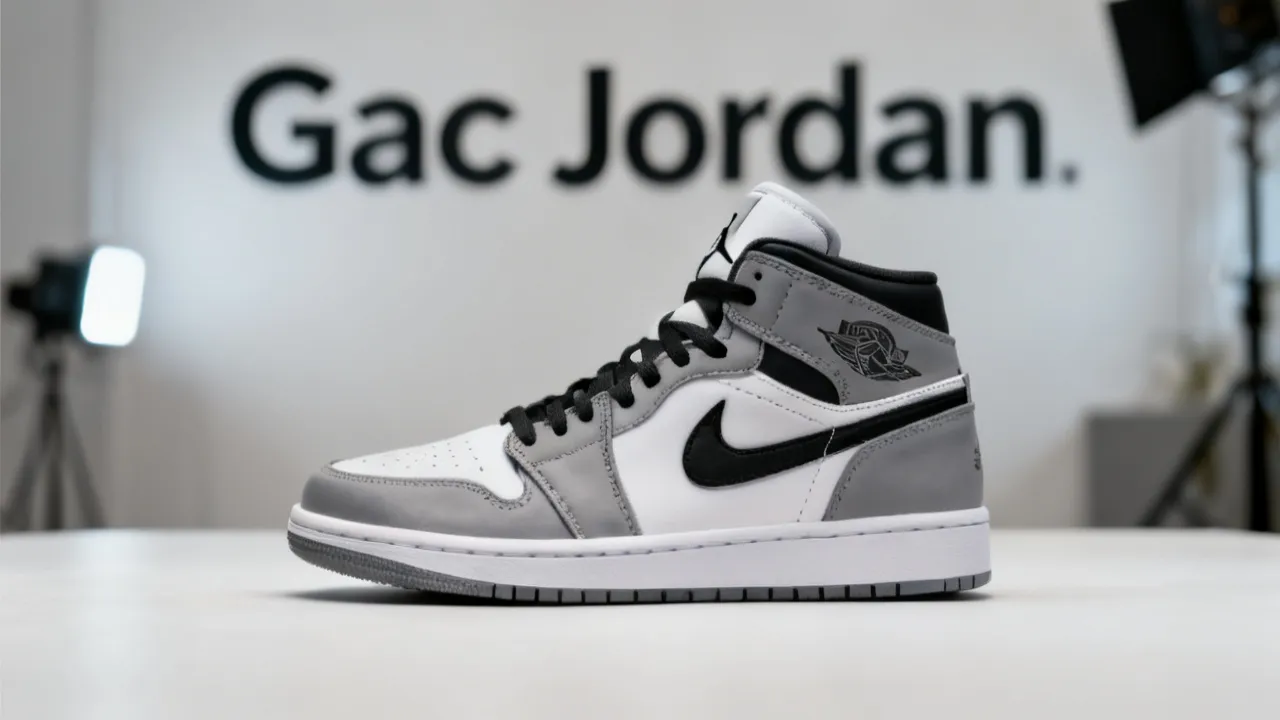
This guide explains how to evaluate “Gac Jordan” as a sneaker-style product—covering pricing considerations, supplier due diligence, and practical selection criteria. Objectively, the term typically refers to Jordan-inspired designs and market listings, where authenticity checks, material specs, and return terms matter. You’ll also find a structured comparison table, requirements checklist, and FAQs for confident buying.
Understanding Doe Ess: Industry Insights and Practical Guidance
This guide explains Doe Ess in an evidence-minded way, covering what it typically refers to, how stakeholders evaluate it, and what to consider before choosing a provider or approach. Objectively, the term is commonly used as a shorthand identifier across discussions, so buyers should verify scope, outputs, and support terms in writing. The article then adds decision conditions, requirements, and FAQs.
A Practical Guide to Londonderry Towers
Londonderry Towers is discussed here as a residential building concept—useful for understanding what buyers and renters typically evaluate. Objectively, “Londonderry” is associated with Northern Ireland and the city region, while “Towers” signals a multi-storey living development. This guide focuses on how stakeholders assess location, building features, costs, and supplier credibility, with conditions and requirements provided later.