This guide explains Espm Ead in an objective, decision-focused way for B2B teams. It outlines what the terms generally represent, how they relate to performance and procurement workflows, and what to verify before buying or integrating solutions. It also includes a practical comparison table, step-by-step requirements, conditions to consider, and industry-style FAQs.
Espm Ead is often best approached as a practical framework for aligning process design, data or system integration, and procurement-style decisioning rather than as a single “feature.” In other words, teams that treat Espm Ead as a package of outcomes—rather than a buzzword—usually do better at onboarding on time and reducing rework. The reason is straightforward: “process” and “execution readiness” are not independent. If you design an operating workflow (who does what, when, with which approvals) without ensuring your data interfaces, deployment model, and audit controls can actually support that workflow, you will eventually face late-stage mismatches.
Similarly, if you focus only on technical integration or only on commercial procurement deliverables, you may miss the operational layer where governance lives: acceptance criteria, escalation steps, responsibility boundaries, and documentation expectations. The best evaluations of Espm Ead typically validate scope, interoperability, and governance early—especially when supplier delivery must be coordinated with implementation constraints, pricing structures, and internal change management.
To make this tangible, think of an Espm Ead evaluation as answering three sets of questions:
When these questions are answered together, the organization gains control—control over timelines, control over costs, control over auditability, and control over operational continuity during change.
In many B2B settings, terms like Espm Ead function as shorthand for a combined approach. One side focuses on structured operational or commercial management (often resembling procurement governance, workflow governance, or program management). The other emphasizes execution readiness—such as data handling, system enablement, and auditability.
Because naming conventions vary by industry, region, and vendor, the responsible way to use Espm Ead language is to treat it as a set of requirements and outcomes rather than as a single fixed definition. A “vendor’s Espm Ead” may reflect a particular methodology, a set of services, or a technical deployment pattern. Your job as an evaluator is to translate that into your business needs and verify it with evidence.
Likewise, “Ead” is commonly used as an abbreviation in multiple domains. In some contexts, it can refer to documentation standards, a deployment method, an analytics layer, a service delivery model, or an engineering/data workflow. The point is not to guess. The point is to confirm intent through vendor documentation, integration specifications, security artifacts, and realistic implementation timelines.
Professionals typically avoid confusion by demanding a “definition packet” during evaluation. This packet should include:
When the vendor provides that material early, evaluations become far more objective. When they do not, organizations usually experience ambiguity-driven risk: different stakeholders interpret “Ead” differently; the supplier assumes a different workflow maturity level; and pricing negotiations become subjective.
When organizations evaluate Espm Ead-related solutions, the highest-value outcomes are usually less about novelty and more about control. Control is a multi-dimensional concept in procurement and operations. In practice, control typically means:
To understand why this matters, consider a realistic scenario. A company might purchase a workflow initiative that includes approvals, notifications, and case tracking. If the technical implementation does not properly handle exception records, or if data mappings are incomplete, operations teams may revert to manual workarounds. Those workarounds can degrade auditability and increase cycle time—directly undermining the original purpose of the solution. Espm Ead evaluation should explicitly address these “real-world” failure modes.
Another commonly underestimated factor is coordination between procurement decisions and technical execution constraints. Suppliers can sometimes deliver software “on paper” but struggle with operational readiness if internal dependencies are unclear. For example:
In practical terms, Espm Ead evaluations succeed when procurement-style diligence is paired with technical validation. Procurement diligence forces clarity in scope and acceptance criteria. Technical validation ensures the solution is operational under real constraints.
Even when Espm Ead is presented as a unified solution, procurement decisions typically depend on how pricing is structured and how suppliers commit to delivery. A well-structured price model can align incentives and reduce disputes. A poorly structured price model often causes late-stage disagreements over what is “included,” what is “extra,” and what changes require additional cost.
To keep evaluations grounded, you should request vendor clarification on at least these pricing and delivery areas. Treat your requests as negotiation-quality inputs, not as simple fact-finding.
If a supplier provides price information, treat it as a starting point. In practice, a quote often includes assumptions. The operational question is whether the quoted structure maps to your real onboarding and governance needs. For instance:
A strong procurement practice is to request pricing-to-deliverables mapping. That mapping is where many ambiguity risks surface. If the vendor can’t connect costs to deliverables and acceptance criteria, the organization should consider whether the evaluation can remain objective.
Professionals typically encounter friction when Espm Ead initiatives assume that integration “just works.” In practice, integration success depends on data models, access controls, workflow triggers, error handling, and documentation quality. The Ead side—depending on what it means in your market—may require alignment with how teams validate inputs, store outputs, and document decisions.
Integration is not merely a technical activity. It is an operational activity. It must support the workflow’s real requirements, including exceptions, delays, retries, and compliance constraints.
To reduce failure risk, ask for evidence and specifics in these areas:
One frequent governance gap is missing or weak exception handling. A workflow often needs to handle cases such as:
Espm Ead evaluation should explicitly test exception paths. Otherwise, teams discover after go-live that the integration works only for “happy path” records. Governance without exception handling becomes fragile; it produces more escalations, more manual work, and less reliable audit trails.
Another governance gap is unclear ownership of errors. When an integration fails, you need to know which party is responsible for triage, whether the error is a vendor defect or an internal data issue, and what evidence must be provided. Your acceptance criteria should include operational playbook expectations and not just technical “it runs” statements.
If you remember only one thing: Espm Ead should be evaluated as a combined operational workflow and execution readiness package. Confirm definitions, validate interoperability, and reconcile pricing with deliverables and acceptance criteria. That discipline helps you avoid common onboarding delays and ensures supplier obligations are measurable.
To make that evaluation real, organizations often build a structured checklist that ties together:
This inverted pyramid approach is effective because it begins with outcomes and then works backward to specifics. You cannot properly evaluate “readiness” without defining readiness in measurable terms. And you cannot properly evaluate governance without connecting governance to concrete technical and operational artifacts.
| Evaluation Area | How Espm Side Is Usually Assessed | How Ead Side Is Usually Assessed | Decision Conditions / Requirements |
|---|---|---|---|
| Definition Clarity | Documented scope of workflow/program management expectations | Clear meaning of “Ead” within the vendor’s architecture or methodology | Vendor must provide a written interpretation tied to your use cases |
| Integration Fit | Process triggers, approvals, and handoffs | Data mapping, interfaces, and deployment readiness | Demonstrate integration with your existing systems and data constraints |
| Pricing Structure | Costs aligned to deliverables and governance activities | Costs aligned to enablement, support, and operational continuity | Break down charges into setup, usage/volume, support tiers, and change requests |
| Supplier Accountability | Milestone-based acceptance and documentation responsibilities | Testing ownership, release strategy, and rollback commitments | Acceptance criteria must be measurable and written into the project plan |
| Security and Governance | Role-based process controls and approvals | Access controls, logging, and retention expectations | Confirm least-privilege access, audit logs, and data handling boundaries |
| Operational Continuity | How workflows continue during onboarding and changes | Monitoring, incident response, and service coverage hours | Request an operational playbook and escalation procedure |
The most reliable approach is to treat Espm Ead evaluation as a structured project discovery process. Below is a step-by-step guide you can adapt for internal governance and supplier negotiations. The emphasis is on converting “claims” into “evidence,” and converting “evidence” into measurable acceptance criteria.
Ask the supplier to define what “Espm” and “Ead” mean in their materials and how those components map to outcomes. Request an explicit mapping document rather than relying on verbal descriptions. The goal is to prevent mismatched expectations between your procurement team, your operations team, and your technical team.
To make this effective, require that the supplier’s definition includes at least:
Write down what success looks like: faster cycle times, fewer manual handoffs, better audit traceability, reduced error rates, or improved decision turnaround. Avoid vague goals like “improve efficiency” without defining baseline metrics and targets.
Good outcome measures usually include both operational metrics and governance metrics, for example:
When you translate goals into measurable outcomes, you can evaluate the supplier’s plan objectively. Otherwise, you may end up with deliverables that look complete but do not achieve business intent.
Request a document that lists deliverables, responsibilities, acceptance criteria, and sign-off milestones. This is where procurement discipline protects implementation quality.
A robust deliverables-and-acceptance matrix should include:
If the supplier resists providing a matrix, that is itself a risk indicator. Resistance often means they want flexibility but you need accountability and measurable commitments.
Run a pilot with representative datasets and realistic workflow triggers. Ensure the Ead component (whatever it means in your context) can handle edge cases: missing inputs, inconsistent records, exception flows, and boundary conditions.
A strong pilot is not just a demonstration; it is a controlled experiment. You should define:
In many teams, pilot success is mistakenly judged by a green check on “integration connected.” But the pilot should also demonstrate governance behaviors: audit logs, correct approval routing, and consistent error handling under stress conditions.
Confirm how roles are managed, which actions are logged, how long logs are retained, and how access is reviewed. This step protects your organization from hidden compliance liabilities and operational risk.
Security and governance validation typically includes:
Make sure your validation plan includes evidence you can store for audits. A good supplier will not only describe security controls; they will provide documentation and demonstration access to relevant systems or logs.
Ensure price information reflects your anticipated onboarding tasks and support needs. Confirm what happens if scope changes—what is renegotiated, and what remains fixed.
To align pricing with effort, you can ask the supplier to:
Many disputes happen when the organization discovers too late that “included” did not include activities like training sessions, environment setup, logging configuration, or additional testing iterations. A deliverables-and-acceptance matrix paired with pricing-to-deliverables mapping reduces the chance of those surprises.
Implementation risk decreases when you establish a go-live schedule and a rollback mechanism. Require clarity on what is reverted and how data integrity is maintained.
Go-live and rollback planning should include:
This is where Ead readiness becomes practical. If the supplier cannot explain rollback and post-release verification clearly, your operational continuity is at risk.
Assign who owns ongoing monitoring, incident triage, and process improvements. If the supplier owns everything, you may become dependent without control. If you own everything, ensure you have the skills and time.
Operational ownership documentation should clarify:
In many organizations, operational ownership is left implicit. That omission often causes confusion after go-live, when questions like “Who approved this change?” and “Who decided this integration mapping was correct?” become urgent. Espm Ead evaluation should force explicit ownership before you rely on the system in production.
In many organizations, procurement processes are already built to manage suppliers through contractual scope, milestones, and acceptance criteria. Espm Ead can complement this by turning those contractual ideas into operational execution—meaning the workflow is not only purchased but also implemented with governance and auditability.
However, an expert caution applies: procurement artifacts alone don’t guarantee correct implementation. The technical side of Ead—whether it refers to deployment enablement, data readiness, or documentation standards—must be validated with tangible evidence such as test plans, integration details, and operational procedures.
This dual lens is what makes Espm Ead discussions useful: it bridges business intent with execution reality. It also reduces the gap between “what the contract promises” and “what the production environment actually does.”
Procurement-style governance typically emphasizes:
Ead readiness, on the other hand, often emphasizes:
When both are combined, organizations gain a stronger governance posture than either approach alone. You can buy a solution that is contractually compliant and technically ready—and you can prove it.
Espm Ead typically represents a combined approach used in B2B contexts to align structured workflow/procurement governance (Espm) with execution readiness such as integration, documentation, deployment enablement, and operational controls (Ead). Because “Ead” can vary by vendor and industry, you should confirm definitions in the supplier’s documentation and architecture materials.
Compare suppliers using the same evaluation lens: scope clarity, integration fit, pricing structure mapped to deliverables, security/governance controls, and measurable acceptance criteria. The decision conditions should be written, not implied. A consistent evaluation template prevents bias and reduces negotiation confusion later.
Request breakdowns for onboarding/setup, usage or volume-based charges (if any), support tier costs, training, and change request handling. Ensure the pricing aligns with the deliverables and the timeline implied by your go-live plan. If the supplier cannot connect costs to deliverables, you should treat it as a risk signal.
In many cases, yes. A pilot reduces uncertainty by testing integrations and workflow edge cases with representative data. It also clarifies whether acceptance criteria are achievable within your operational constraints. Even for mature suppliers, pilots reveal mismatches in assumptions and exception handling.
Verify role-based access, audit logging, data handling boundaries, retention expectations, and the escalation path for operational incidents. These controls should be validated during onboarding, not only described in marketing material. The best suppliers will provide evidence and allow you to review or test governance artifacts.
Use a deliverables-and-acceptance matrix with milestone sign-offs. Require documented responsibilities for integration testing, documentation, and operational readiness—then measure progress against those criteria. Also confirm what happens when milestones are missed and whether there is a remediation plan.
Common issues include unclear definition of Espm vs. Ead responsibilities, mismatch between quoted pricing and real onboarding effort, inadequate integration testing, weak governance (especially around approvals and auditability), missing rollback planning, and insufficient clarity on operational ownership. Many failures are avoidable when evaluation includes pilot testing and evidence-based acceptance criteria.
If your procurement or operations are influenced by local delivery realities, “nearby” should be considered in terms of logistics, time zones, and stakeholder availability—without assuming capabilities. Always validate delivery responsiveness and support coverage independently of geography. Also clarify how support operates across time zones and how escalation is handled outside business hours.
To keep guidance consistent with professional procurement and risk management practices, the evaluation approach aligns with widely accepted governance concepts documented by reputable standard-setting and professional bodies. For information security governance, organizations commonly reference frameworks such as ISO/IEC 27001 and related guidance. For service management controls and incident governance, organizations often reference ISO/IEC 20000 or similar service management frameworks. Use your internal compliance team to map these to your policies.
In vendor evaluations, reliance should be placed on vendor-provided evidence and documented test results rather than promotional statements. Where industry metrics are relevant, cross-check them using credible analyst reports, official research, and published standards from recognized organizations. Your procurement team can define which sources are acceptable evidence for internal decision-making.
Additionally, for objective evaluation of Espm Ead claims, consider requiring:
These artifacts ensure that “readiness” is not only asserted but demonstrated.
Espm Ead becomes valuable when treated as a disciplined evaluation of workflow governance plus execution readiness. Your highest-confidence outcomes come from confirming definitions, aligning pricing with deliverables, validating integration through a controlled pilot, and ensuring governance controls—access, logging, and escalation—are operational from day one. If you build your supplier decision around measurable acceptance criteria and evidence-based validation, you are much more likely to secure continuity, reduce rework, and maintain confidence through the lifecycle.
Ultimately, the main idea is not to treat Espm Ead as a magic phrase. Treat it as a structured method for combining operational process clarity (who does what, under which approvals) with technical execution readiness (integration, deployment, documentation, logging, and rollback). When both layers are verified and anchored to contractual accountability, Espm Ead moves from “marketing language” to a measurable decision framework.
To implement that framework effectively, keep your evaluation tightly connected to artifacts: deliverables-and-acceptance matrices, integration evidence, security and logging documentation, operational playbooks, pilot results, and rollback plans. When those artifacts exist, you can make a decision confidently—and you can defend that decision during audits, compliance reviews, and internal governance cycles.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans

Explore the Tranquil Bliss of Idyllic Rural Retreats

How to Make Lasting Memories at Disneyland Attractions

Affordable Phones and Plans for Seniors

Affordable Full Mouth Dental Implants Near You

Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!

Discovering Springdale Estates

Unveiling RS Sul Telecom Services

The Guide to Car Trading

Understanding Lato Sensu Education
Lato Sensu is a term used to describe a type of specialized education, typically in the context of postgraduate studies. It emphasizes a flexible, broad approach to learning compared to more narrowly defined courses. This article delves into the significance, scope, and benefits of Lato Sensu programs, particularly how they cater to professionals seeking career advancement.
Unlocking the Secrets of Wizard Lessons
Wizard Lessons offer a glimpse into the mystical world of magic, providing structured learning experiences for aspiring wizards. These lessons cover various aspects of magic, from spell casting to potion making, and are deeply rooted in both tradition and evolving magical practices. Aspiring wizards can delve into these teachings to enhance their magical prowess and understanding of the enchanted arts.
Understanding Lato Sensu Courses
Lato Sensu refers to postgraduate courses offering specialized education, often linked to practical experiences and professional enhancement. These programs emphasize advanced learning tailored to students' chosen fields, with flexible formats to accommodate diverse educational goals and local contexts. This article explores the significance, structure, and advantages of Lato Sensu programs for aspiring professionals.
Understanding Lato Sensu Education Courses
Lato sensu education courses are specialized postgraduate programs offering practical skills and knowledge in specific fields. Distinct from stricto sensu programs focusing on academic research, lato sensu courses are typically shorter and professionally oriented, making them attractive to those seeking career enhancement. This article delves into the intricacies of lato sensu education, exploring its benefits, structure, and global perspective.
Understanding PECB AAT Certifications
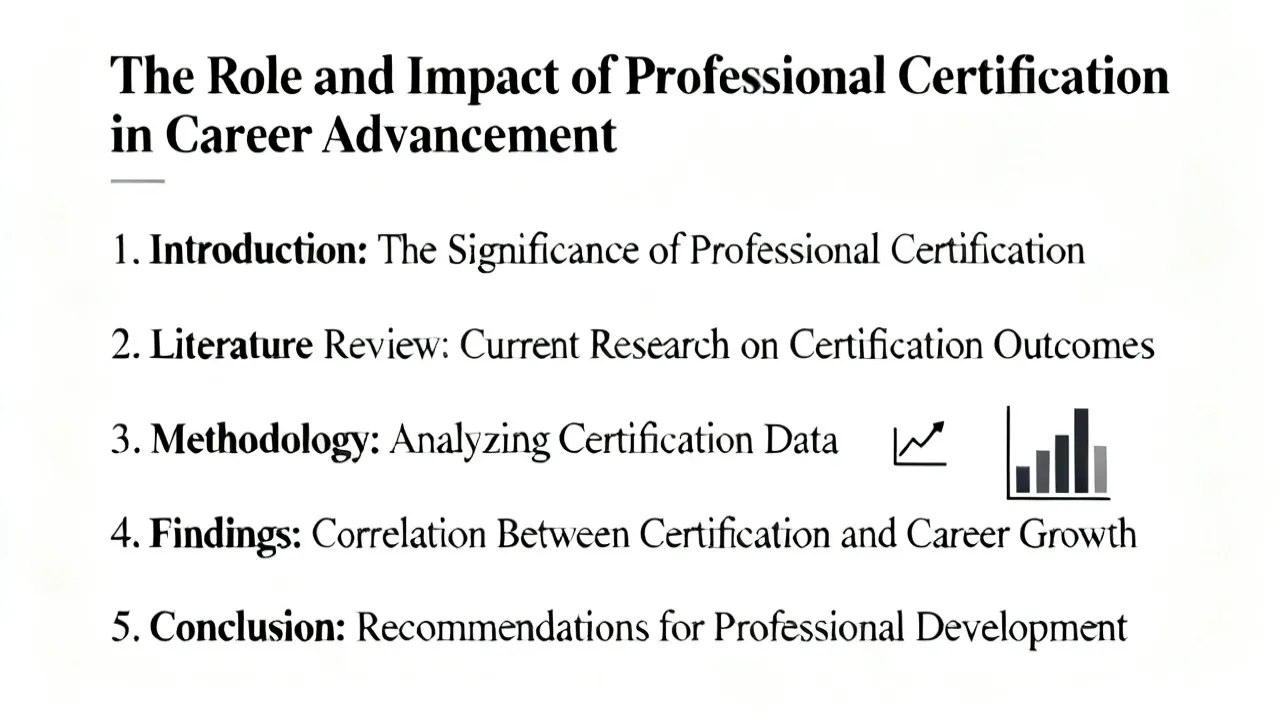
This article offers an in-depth analysis of PECB AAT certifications, renowned for providing a standardized framework for auditing, assessment, and training in various professional sectors. It highlights the importance of these certifications in ensuring industry compliance and enhancing career opportunities. From certification pathways to FAQs, explore how these qualifications uphold standards and elevate expertise in their fields.
Understanding Lato Sensu Education
This guide explores the essential aspects of Lato Sensu programs, which are critical post-graduate courses focusing on specific professional skills enhancement. Typically found in Brazilian education, these programs differ from Stricto Sensu courses by emphasizing practical skills over theoretical research. The article analyzes the elements critical to choosing a Lato Sensu course, such as institution reputation, course content, and potential career outcomes.
