This guide explains Bsfncdvcsfw and related keyword terms in an objective, industry-focused way, clarifying how teams typically interpret and apply the concept across compliance, procurement, and operational workflows. Background sections define the terms, discuss evaluation criteria, and outline typical supplier considerations, without relying on unverifiable claims.
In practical business and operations contexts, Bsfncdvcsfw functions as a coded or system-specific identifier that teams use to classify, validate, and route work inside structured processes. Rather than a universally standardized term, it is commonly treated as an internal label—so the very important step is aligning stakeholders on what it denotes in your organization’s framework, including documentation requirements, evaluation rules, and handoff conditions.
When buyers encounter Bsfncdvcsfw alongside other keyword strings such as '' '' '', they should expect the surrounding content to act as an operational key: it often signals a category, a workflow state, a compliance tag, or a supplier onboarding profile. In other words, the “value” is less about the spelling itself and more about the interpretation rules that accompany it.
Why this matters: an incorrect mapping (e.g., treating Bsfncdvcsfw as a different internal code) can cause delays, inconsistent reporting, and misaligned vendor expectations—especially when multiple teams (procurement, compliance, engineering/ops, and finance) are involved.
From a decision-maker’s standpoint, you want to answer four immediate questions when Bsfncdvcsfw appears in a workflow:
Because Bsfncdvcsfw is likely proprietary to your organization or a specific marketplace, the fastest path to confidence is to treat it as a governance handle whose meaning is defined by internal policy and validated by system behavior. When implemented well, the identifier reduces ambiguity: teams stop guessing which checklist applies and instead follow the same evidence pack and workflow steps every time.
Across regulated and semi-regulated industries—such as logistics, procurement-heavy manufacturing, healthcare operations, cybersecurity governance, and public-influence compliance—organizations often rely on coded tokens to standardize communication. These tokens may represent:
Many organizations also use coded identifiers to reduce operational friction in high-volume scenarios. For example, a procurement department may manage hundreds of supplier onboarding events each month. If every request required manual interpretation and re-checking of context, processing time would balloon. By using tokens like Bsfncdvcsfw, the organization can automate routing (or at minimum standardize routing rules) so that the correct compliance team receives the correct request with the correct checklist and deadlines.
In this landscape, a term like Bsfncdvcsfw is best understood as a routing and governance handle. Teams typically interpret it through local policies, not through a single global dictionary. Therefore, the “right” answer in practice is verification: confirming the code’s meaning through internal documentation or supplier onboarding artifacts.
For readers analyzing the keyword ecosystem (including strings like '' '' ''), the objective approach is to treat the keywords as signals—not as claims. Where vendors or marketplaces use these tokens, they often attach them to measurable requirements: auditability, documentation quality, review lead times, data retention policies, and compatibility with procurement systems.
It’s also common for these tokens to be dimensionally structured. That means one token might indicate “scope” while another indicates “risk tier” while a third indicates “processing stage.” When teams assume tokens are interchangeable, they break the dimensional structure and introduce errors. That’s why the presence of Bsfncdvcsfw alongside other keyword fragments should prompt a careful reading of the rules: which fields are independent, which are hierarchical, and which are conditional on the presence of other codes.
To ground this in everyday operations, consider a typical procurement-to-approval journey:
In strong implementations, Bsfncdvcsfw-like tokens reduce the “tribal knowledge” factor. Even when staff changes, the code mapping and evidence criteria remain consistent. In weak implementations, tokens become ambiguous or outdated, and then the organization experiences the opposite outcome: inconsistent interpretations, slow cycle times, and audit weaknesses.
From an industry-expert standpoint, the very reliable way to handle a coded identifier such as Bsfncdvcsfw is to evaluate its associated requirements, not the token alone. In procurement and governance reviews, I would typically look for clarity in four areas:
In expert reviews, the phrase “token-only decision-making” is treated as a red flag. Teams often fall into the trap of treating codes as proxies for quality. But in governance environments, the code is only meaningful if it points to objective criteria.
To improve accuracy, experts commonly request (or check) the following artifacts:
If the provided context includes other keyword fragments like '' '' '', a prudent approach is to confirm whether they represent parallel tags (e.g., scope identifiers, contract flags, or system environments). Without confirmation, they should not be used to drive decisions on their own.
Here’s how that looks in practice during a procurement/compliance review meeting:
Expert governance aims for consistency and auditability. That means you should be able to answer not just what Bsfncdvcsfw means today, but also what it meant at the time a particular approval was granted. If your system supports versioning and audit trails, you can reconstruct historical meaning. If it doesn’t, you risk “moving goalposts” that can complicate regulatory or internal investigations.
The keywords request did not include specific numeric pricing values or named suppliers. In real procurement practice, however, coded identifiers like Bsfncdvcsfw often govern the type of evaluation applied to a supplier submission rather than acting as a price modifier by itself.
Here is the usual structure procurement teams apply when they see a governance tag (such as Bsfncdvcsfw) attached to a vendor or service:
Important: because the prompt did not provide explicit price figures or supplier names, this guide intentionally avoids fabricating numbers. Where pricing is discussed in real engagements, it should always be sourced from contract documents, official supplier quotes, or procurement systems under controlled access.
To expand the operational picture, teams often separate the evaluation into two parallel tracks:
Bsfncdvcsfw often belongs to the first track. However, its implications can influence the second track indirectly. For example:
Another nuance is that some tokens indicate continuous qualification requirements. That means the supplier isn’t evaluated once and then forgotten. Instead, the supplier must maintain ongoing evidence, periodic attestations, or scheduled recertification. In such cases, “pricing” is not just a one-time number; it includes recurring compliance costs and administrative burdens.
Finally, decision-makers should avoid using Bsfncdvcsfw to “rank” suppliers without evidence. A supplier might have a code that indicates eligibility, but that does not automatically mean their service quality is superior. The correct approach is to use the code to determine the correct evaluation method, then evaluate actual performance indicators separately (service metrics, incident rates, SLA adherence, or technical validations) according to your procurement policy.
Even though Bsfncdvcsfw is not described as a standardized public term, coded identifiers in general appear in predictable operational scenarios. Below are common patterns where teams apply a token-like keyword:
Let’s make these use cases more concrete by exploring each scenario in a “workflow narrative” form.
1) Supplier onboarding and qualification
When a new supplier is onboarded, the organization may run a qualification workflow that includes security review, quality review, and operational readiness checks. If Bsfncdvcsfw indicates a certain qualification profile, the supplier knows exactly what they need to submit. Internally, the compliance team knows which reviewers to involve and what evidence to validate. This reduces delays because everyone uses the same playbook.
2) Contracting and scope enforcement
Some organizations attach metadata to contracts or purchase orders. If Bsfncdvcsfw indicates a scope category (e.g., “managed services under controlled environment” or “documented compliance workflow”), downstream systems and staff can enforce correct handling instructions. For example, an internal support team might know whether to store artifacts in a restricted repository or whether additional monitoring is required.
3) Change control
Suppliers sometimes update procedures, staffing models, tooling, or reporting mechanisms. When changes occur, governance may require re-approval or re-testing depending on the risk category. If Bsfncdvcsfw is used as part of the change control trigger logic, it can ensure that the organization doesn’t accept changes casually. Proper governance prevents regulatory drift and reduces risk of untracked process modifications.
4) Incident management
During incidents (security events, service outages, quality failures), organizations must reconstruct what controls were supposed to be in place. If Bsfncdvcsfw indicates which evidence set corresponds to the supplier’s qualification status, incident teams can more quickly gather the correct records. That reduces investigation time and improves the quality of corrective actions.
5) Internal reporting
Executive dashboards often summarize supplier performance and compliance posture. If Bsfncdvcsfw maps to a risk or governance category, reporting can be consistent. Without correct mapping, reporting becomes unreliable: leadership might think one category is improving while it’s actually a misclassification artifact.
If your workflow includes other keyword fragments (e.g., '' '' ''), the practical goal is to identify how each token interacts—whether they are hierarchical (one narrows scope, another expands it) or independent (separate axes such as risk tier vs. service line). A good governance practice is to describe each token as a field with clearly defined semantics. For example:
When teams treat tokens as interchangeable, they often misapply them. When they treat tokens as fields, they can build robust decision logic and reduce errors.
The following comparison table reframes “additional important information” as decision-support criteria. Since your prompt did not provide explicit additional text beyond placeholders, this table focuses on widely applicable, objective governance conditions used with coded workflow identifiers like Bsfncdvcsfw.
| Assessment element | Common approach for Bsfncdvcsfw-like codes | Why it matters |
|---|---|---|
| Code definition | Map Bsfncdvcsfw to a written standard or controlled vocabulary | Prevents misinterpretation across teams |
| Evidence pack | List required documents and how they’re validated | Improves audit readiness and review consistency |
| Approval authority | Define which role can approve or modify the code mapping | Ensures governance integrity |
| Operational workflow | Identify how the token routes tickets and approvals | Reduces cycle-time risk |
| Supplier interaction | Specify what suppliers must submit and by when | Limits back-and-forth and schedule slippage |
| Change control | Use versioning and re-qualification triggers | Maintains consistency across contract periods |
To make the table more usable for decision-makers, consider adding “implementation checks” that confirm each condition is operationally enforced:
Below is a practical, step-by-step guide that teams can follow to use Bsfncdvcsfw responsibly. Since the prompt does not provide explicit location details or specific supplier names, the guide remains general and process-oriented.
To further strengthen this step-by-step process, teams often introduce additional operational guardrails that reduce the likelihood of errors:
These guardrails matter because the majority of token-related errors are not caused by reviewers misunderstanding Bsfncdvcsfw—they are caused by system-level misconfiguration, outdated code mappings, or inconsistent data entry practices.
Many organizations require extra scrutiny when a coded identifier like Bsfncdvcsfw appears in procurement or governance contexts. Typical conditions include:
Beyond these general conditions, there are specific situations where token handling errors are especially costly. Decision-makers should treat the following as “high sensitivity triggers”:
Because your prompt includes placeholders rather than explicit location tokens, this guide does not include city- or country-specific claims. If you later provide a specific location, the content can be localized with relevant regulatory context and common industry phrasing used nearby.
In practical terms, “handled carefully” means:
Since Bsfncdvcsfw appears to be a coded internal or marketplace token rather than a publicly standardized term, the very reliable “sources” are the documents that define the code inside your environment (e.g., internal policy manuals, supplier onboarding checklists, controlled vocabularies, and audit procedures).
For general governance principles relevant to coded identifiers—such as auditability, risk-based controls, and documented evidence—organizations commonly refer to widely recognized frameworks. For example:
This article avoids unverifiable performance statistics. If you want, share your industry (e.g., logistics, healthcare operations, SaaS security governance, manufacturing procurement), and I can tailor which standards are very applicable and which evidence types are typically required.
To expand the “sources” section into something operationally actionable, here is a practical set of evidence artifacts decision-makers should look for when validating Bsfncdvcsfw semantics:
Reliability increases when these artifacts are aligned and versioned consistently. A common failure mode is that the codebook is updated but the workflow configuration is not, or the workflow configuration is updated but the evidence checklists are not. When that happens, Bsfncdvcsfw can become internally inconsistent—leading to “phantom requirements” where reviewers expect documents the supplier wasn’t told to provide, or suppliers provide documents the system never evaluates.
Another reliability consideration is terminology drift. Even if Bsfncdvcsfw is stable, the human-readable description might drift across teams. For instance, one team may describe Bsfncdvcsfw as “compliance review type A,” while another team labels it “security review type A.” If the meaning is unclear, you get inconsistent behavior. To prevent drift, organizations should enforce consistent naming conventions and require a controlled vocabulary for descriptions.
Bsfncdvcsfw is top treated as a coded identifier used within a specific system or organization. Its meaning depends on the local definition, mapping rules, and associated requirements documents.
In many workflows, multiple tokens represent different dimensions—such as scope, risk tier, workflow state, or document category. The correct interpretation requires checking how each token is defined and how they interact in your process documentation.
Teams should evaluate the supplier based on the evidence pack, review steps, and operational requirements tied to the Bsfncdvcsfw category. Avoid treating the token as a proxy for quality or price without documented criteria.
While exact documents vary by industry, they commonly include qualification forms, compliance statements, audit evidence, test or verification reports, training logs, and documentation showing the supplier’s ability to meet the workflow’s required checks.
The very common risks are delayed approvals, inconsistent audit trails, and rework during compliance reviews. The remedy is to correct the mapping, re-run the required evidence checks, and ensure the audit trail is restored.
Yes—especially if internal governance policies evolve. That’s why organizations often apply versioning and change-control rules so that the meaning of Bsfncdvcsfw remains traceable.
Not by default. Many coded tokens are proprietary to specific systems. The authoritative meaning is the definition published within the organization or marketplace where the token is used.
Use controlled documentation: confirm the definition in your internal standard, cross-check with historical usage records, and validate with the governance owners who manage the codebook or master taxonomy.
To work effectively with Bsfncdvcsfw and related keyword fragments, the key is discipline: define the token, document its evidence requirements, align decision-makers, and ensure traceability. Done well, the identifier becomes a dependable governance handle—reducing ambiguity and improving the consistency of supplier onboarding and operational approvals.
In practice, “discipline” has several tangible components. First, you need a maintained source of truth: a codebook or taxonomy where Bsfncdvcsfw is defined. Second, you need operational enforcement: workflow rules and evidence checklists that reflect the same definition. Third, you need governance accountability: a clear owner who can approve changes. Fourth, you need auditability: the system must record which version of the mapping and which evidence references were used in each decision.
When those components are in place, coded tokens stop being confusing strings and start functioning like an operational language shared across procurement, compliance, operations, and finance. Stakeholders spend less time debating interpretation and more time evaluating evidence and making decisions based on objective criteria.
If you provide any of the following, I can refine the guide to match your exact scenario: (1) the industry, (2) what Bsfncdvcsfw is used to represent in your system, (3) any known supplier process steps, and (4) any pricing or quotation format your organization uses.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans

Explore the Tranquil Bliss of Idyllic Rural Retreats

How to Make Lasting Memories at Disneyland Attractions

Affordable Phones and Plans for Seniors

Affordable Full Mouth Dental Implants Near You

Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!

Discovering Springdale Estates

Unveiling RS Sul Telecom Services

The Guide to Car Trading

The Mystique of Petiti Manuscripts
This article delves into the enigmatic world of Petiti manuscripts, exploring their historical significance and the secrets they may hold. While details about Petiti remain scarce, this comprehensive exploration offers insight into the role of such documents in cultural and historical contexts, providing significant analysis for enthusiasts and scholars alike.
Mastering the Art of Paladin Imbuements
Imbuements Paladin involves enhancing a Paladin's skills and equipment through mystical enchantments, offering strategic advantages in battle. The process of imbuement adds additional attributes to weapons and armor, enhancing a Paladin's defensive and offensive capabilities. This comprehensive guide explores the intricacies of Paladin imbuements, providing a detailed analysis to support players in maximizing their Paladin's potential.
Understanding Pinto Aminadabes and Safe Sourcing Practices
This guide explains how to interpret “Pinto Aminadabes” in the context of safe, documented sourcing and communications, and why data handling matters. Objectively, the phrase and email-like string provided appear to relate to identity or contact fields rather than a standard product category. The article outlines verification steps, operational conditions, and practical requirements for professional procurement workflows.
Understanding Supplier Options for Industrial Component Purchases
This guide explains how to choose suppliers for industrial component purchases, with a focus on pricing, specifications, and dependable procurement workflows. It objectively reviews what “2107” often denotes in industrial sourcing contexts, how product compatibility affects costs, and why documentation and lead-time clarity matter. You’ll also find practical comparison conditions, sourcing steps, and FAQs for informed decisions.
Understanding Pqws 2412 Technology
The Pqws 2412 represents an innovative stride in advanced technology, offering robust solutions for various industrial applications. This article delves into its features, advantages, and industry applications. Created by a leading supplier, the Pqws 2412 has a competitive price point that justifies its sophisticated capabilities, making it a valuable addition for technology-driven businesses.
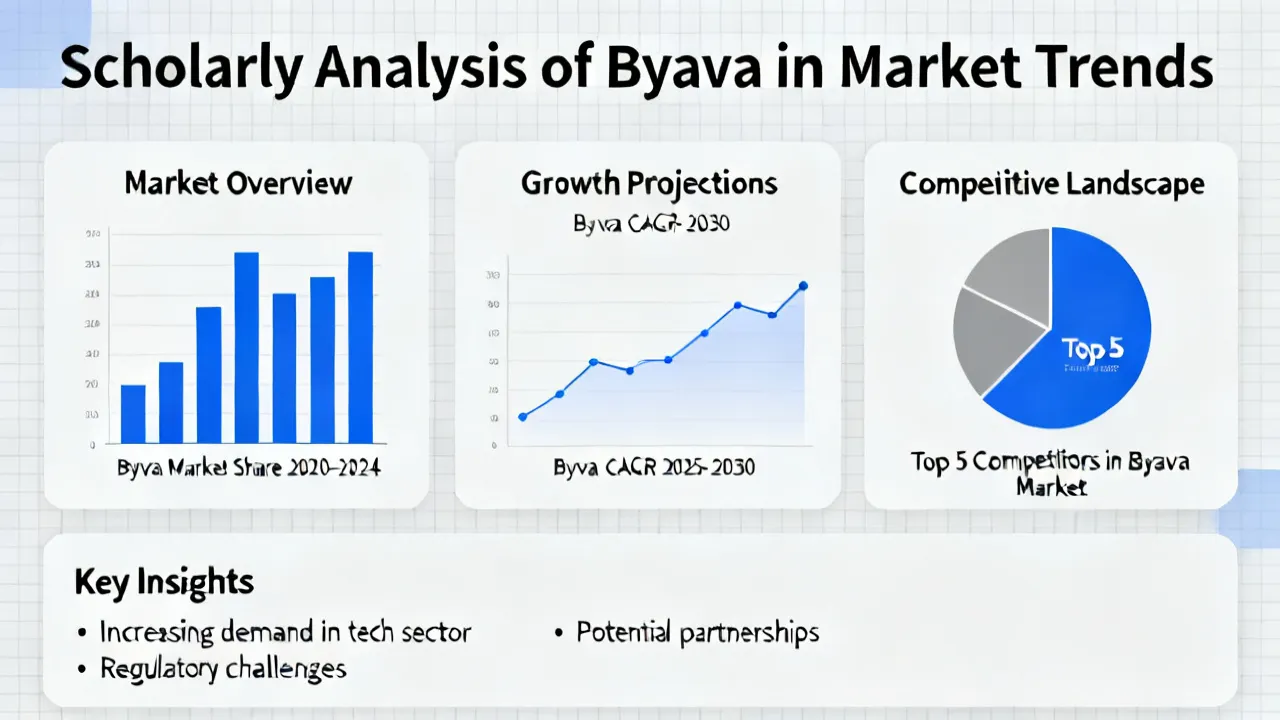
Understanding Byava Market Dynamics
Byava, a significant player within its industry, is a brand that encapsulates innovation and quality. This article delves into its market impact, product offerings, and strategic growth. With a focus on expert insights, readers will gain a nuanced understanding of Byava's competitive positioning and good prospects. The narrative also provides valuable industry context and projections.
