Payment Processing Systems are the backbone of secure, efficient transactions across cards, wallets, and bank rails. This guide objectively explains how modern systems manage authorization, tokenization, risk checks, and settlement. You’ll also find a practical comparison table of common payment approaches, key selection conditions, and a step-by-step implementation guide for operational readiness.
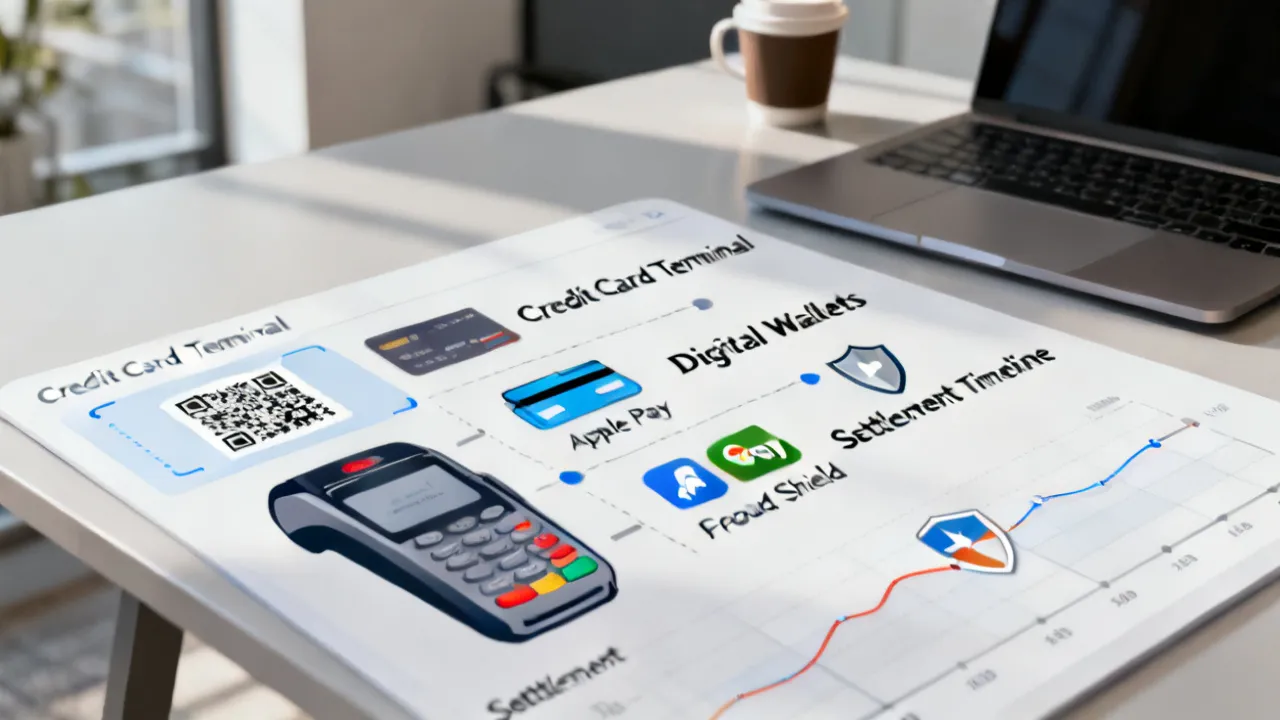
Payment Processing Systems determine how reliably a business accepts, secures, and settles customer payments across cards, digital wallets, and bank transfers. At an expert level, the very critical evaluation factors are security controls (especially for card data handling), transaction lifecycle reliability (authorization, capture, settlement, and reconciliation), risk and compliance features, and integration fit with your checkout, accounting, and ERP stack.
In practical terms, a good Payment Processing System reduces payment failures, limits fraud exposure, and improves accounting accuracy—without forcing operational workarounds. This is especially important for businesses that serve international customers, operate multiple sales channels, or handle high volumes during peak demand.
However, “performance” in payments is not a single number. It includes conversion impact (approval rates and friction), operational stability (how cleanly the system delivers events, how safely retries work), financial control (how accurately settlement reports map to revenue records), and customer experience (how quickly refunds resolve, how transparently support can handle issues, and how consistently payment methods behave). When these elements are aligned, a Payment Processing System becomes a durable growth enabler rather than a recurring source of operational stress.
Historically, payment acceptance was treated as a narrow technical capability. Today, Payment Processing Systems function as operational infrastructure. They coordinate multiple stages of the transaction and provide the reporting surfaces that finance and operations teams need.
For objective background: payment flows typically involve (1) customer authentication and authorization requests, (2) issuer and network checks, (3) capture of funds, (4) clearing and settlement, and (5) downstream reconciliation and chargeback handling. Each stage can create delays or discrepancies if the system, integrations, or configuration are misaligned.
In industry practice, vendors differentiate themselves through how they handle data minimization (e.g., tokenization and secure vaulting), support fraud screening, provide durable webhooks and event logs, and deliver transparent fee structures that match actual processing behavior (authorization rates, payment method mix, refund/chargeback patterns).
To understand why this matters, consider what happens when payment systems fail operationally. If capture timing is inconsistent, finance reconciliation becomes noisy. If webhook payloads are unreliable or undocumented, customer support is forced into manual detective work. If idempotency is missing or poorly implemented, retries can generate duplicate charges—or cause refunds to fail because the system cannot confidently link requests to the original payment. In that environment, performance is not simply “good uptime.” It is the absence of avoidable human labor and errors.
At an organizational level, Payment Processing Systems also influence governance: how risk rules are approved, how exceptions are handled, and how you monitor the system across time. A mature payment program has clear ownership for fraud tuning, incident response, and dispute management. The payment platform you choose can either make governance straightforward or complicate it with fragmented tooling.
An expert evaluation usually breaks Payment Processing Systems into components you can verify during due diligence:
Beyond listing features, you want to validate operational behavior. Feature checklists can be misleading because vendors can “support” partial capture yet behave differently under network failures, timeouts, or provider-specific routing. Therefore, due diligence should focus on how the system behaves under realistic conditions: what happens when a customer’s browser loses connectivity mid-payment, how retries are handled, how status transitions are represented, and how you receive the truth of what occurred.
To make this concrete, teams often evaluate the following during PoCs: (1) whether the payment intent object is the authoritative source of truth, (2) whether capture is allowed only after authorization is valid, (3) whether refunds can be issued before settlement or only after capture, and (4) how the system differentiates between “canceled,” “expired,” and “failed” states. These distinctions directly affect how you write business logic and how you reconcile financial outcomes.
Payment Processing Systems must handle sensitive data responsibly. The very important security question is not simply whether a vendor “is compliant,” but how cardholder data is handled in your architecture. In many modern implementations, businesses aim to avoid direct storage or processing of raw card data by using tokenization and secure hosted fields.
For context, PCI DSS (Payment Card Industry Data Security Standard) sets requirements for organizations handling card data. Industry bodies and payment providers reference PCI guidance to reduce breach risk. Businesses should confirm whether their implementation approach reduces PCI scope through tokenization, hosted checkout, or other compliant patterns.
Objective requirement: validate that your chosen system supports secure data handling patterns appropriate to your integration model (hosted checkout vs. embedded forms vs. API-led tokenization). Also confirm encryption, access controls, audit logs, and vulnerability management practices.
At an expert level, you also want to consider the security boundaries created by your integration decisions. For example:
Security also includes operational security: who can view payment logs, who can export transaction data, how admin access is restricted, and how audit trails are stored. A payment team often needs to investigate payment anomalies, but investigation requires privileged access. If the vendor provides granular role-based access controls and audit logging, investigations remain controlled and compliant. If not, you may have to redesign your internal processes or accept higher security risk.
Finally, security is not only about card data. Payment systems can process personal data for billing and identity verification, and risk engines can ingest signals like device fingerprinting or behavioral patterns. Strong vendors typically support data retention controls, provide clear documentation on what signals are used, and help you align with privacy obligations (including consent and purpose limitation where applicable).
Many payment failures are not “security issues,” but integration and lifecycle misconfigurations: missing webhook handlers, incorrect idempotency keys, or mismatched refund flows. Payment Processing Systems should provide deterministic behavior so finance teams can reconcile daily activity with minimal manual adjustment.
When assessing transaction lifecycle reliability, consider the following:
It helps to think of the transaction lifecycle as a state machine. If your integration assumes one sequence of events but the platform emits another (especially in failure scenarios), you can end up with “phantom” outcomes: payments that appear captured in your system but not actually settled; refunds that appear complete but are pending; disputes that are filed but not associated with the correct evidence set.
Therefore, beyond verifying that webhooks “work,” you should check:
Many organizations only discover lifecycle unreliability after migration go-lives, when their accounting and support teams are busiest. That is why a proof-of-concept should include failure and recovery tests: simulated timeouts, intentional webhook endpoint failures, duplicate “create payment” requests, delayed capture operations, and refund requests after a partial fulfillment scenario.
A recurring difficulty in Payment Processing Systems selection is that fee structures can be difficult to interpret. While this guide does not use unverified pricing claims, the expert approach is to require clarity on the components of total cost and how they map to your expected transaction behavior.
In due diligence, ask for a detailed schedule that typically includes acceptance fees, processing rates, and possible additional charges related to cross-border volume, payment method diversity, chargebacks, refunds, or service tiers. Because merchant activity patterns vary, you should request a pricing model that can be benchmarked against historical transaction data.
For decision-making, use an “apples-to-apples” approach: compare not only headline rates, but also fee components tied to operational realities (refund volume, dispute frequency, and whether your system reduces failed payment attempts through optimization features).
Also ensure you understand how pricing applies under different lifecycle stages. Some providers charge based on authorizations, some on captures, and some on settled amounts. If your business uses preauthorization and later capture, or partial capture workflows, you need to know how those scenarios are priced.
At an expert level, finance leaders should ask for a fee worksheet mapping each fee component to measurable metrics. For example:
A transparent system is not only one with low headline rates. It is one that provides enough visibility to reconcile fees to outcomes. If your monthly statements are opaque or require heavy manual reconciliation, you lose control over your true unit economics and increase the cost of financial operations.
Payment Processing Systems are frequently judged at the moment of checkout, but their good value depends on integration and operations. A system should support:
When evaluating integration fit, involve stakeholders beyond engineering—finance, customer support, and fraud review teams. This is often where gaps appear: the payment system may function technically, but staff may lack the data they need to resolve issues quickly.
To avoid such gaps, you should require that integrations provide consistent “business keys” across systems. For example, if your storefront creates an internal order ID and your payment intent includes a vendor payment ID, you need a reliable mapping strategy between them. Finance should be able to answer: “Which order generated this transaction? Which refund corresponds to which order? Which disputes relate to which customers and which line items?”
Furthermore, operational workflow fit includes how your system handles edge cases:
Mature payment platforms provide explicit guidance for these cases, often including recommended patterns for idempotency keys, event tracking, and polling fallback mechanisms.
Payment Processing Systems that support multiple payment methods help businesses match customer preferences. Common options include cards and digital wallets. Some businesses also consider bank transfer flows, especially for higher-ticket purchases or where local payment methods materially impact conversion.
From an objective perspective, expanding payment method coverage can improve conversion, but it also adds operational complexity. Each method can have different authorization/capture semantics, settlement timelines, and dispute characteristics. Therefore, it is important to measure not only approval rate but also downstream metrics like refund processing time and dispute handling effort.
Customer experience also depends on how the system communicates. Good platforms support real-time user-facing feedback (within the limits of PCI scope) and provide “reason codes” or internal classification signals that you can use to display appropriate messages. Poor platforms may provide generic failure messages that lead to repeated attempts, increasing costs and frustration.
An expert evaluation therefore looks beyond payment method availability and assesses:
In multi-channel businesses (web + mobile app + POS), consistency is crucial. If the payment method selection differs between channels or the lifecycle statuses are mapped differently, teams struggle to maintain unified customer service and analytics.
Fraud controls in Payment Processing Systems are typically configurable. The goal is not to eliminate risk entirely—because false positives can harm conversion and customer trust. Instead, systems should offer layered defense: baseline controls, adaptive signals, and policy tuning.
When assessing risk tooling, look for:
Very importantly, ensure that fraud policy changes are governed. Update controls through documented procedures and test in staging to prevent sudden shifts in approval rates.
An expert fraud program also treats risk tooling as a continuous learning system. That means you need feedback loops:
Another subtlety is that fraud controls must be aligned with your business operations. For example, if your business fulfills goods quickly after capture, then your cutoff for risk acceptance must be stricter—or you may need a “review queue” that delays fulfillment for suspicious transactions. The payment platform should support these workflows by providing the signals you need and enabling review processes.
Also consider authentication and network-level signals. Payment platforms may support features like 3D Secure flows for card payments. While such features can reduce fraud, they can also introduce friction and potentially reduce conversions. Therefore, you should evaluate how authentication enforcement can be configured and measured, including how often it triggers and how customers behave during additional verification steps.
For businesses serving international customers, Payment Processing Systems must address cross-border complexity. Currency, network differences, local payment method availability, and varying settlement timing can create reconciliation challenges.
Objective top practice includes:
Even when a merchant does not operate “nearby” a specific location in the text, localization is still relevant in user experience, documentation clarity, and operational workflows. Clear terminology for support teams reduces time-to-resolution and prevents avoidable disputes.
International performance also depends on operational readiness for different settlement timelines. Some payment methods settle quickly; others require longer clearing periods. Your finance reconciliation schedule must accommodate these differences so that “pending” states are correctly interpreted.
For global merchants, these additional factors matter:
In practice, global merchants often need a standardized “payment event model” in their internal systems. That model includes fields for original amount, settlement amount, settlement currency, exchange rate reference (if applicable), fees, and refund linkage. A Payment Processing System that gives consistent data structures makes that standardization easier.
Because the payment sector is competitive, you should not accept high-level promises without verification. Ask vendors about operational practices and provide measurable requirements such as webhook reliability approach, incident response process, and support coverage during peak periods.
For high-stakes decisions, consider conducting a proof-of-concept with representative transaction scenarios: retries, refunds, partial captures, and failure conditions. Objective evaluation reduces surprises after go-live.
Reliability is a multi-dimensional concept. You can test technical reliability (webhook delivery, API availability) and operational reliability (support responsiveness, incident communication). Both affect business performance.
To verify claims objectively, request:
Additionally, for larger enterprises, you should request that the vendor provide a migration plan with compatibility guarantees. That includes how API versions are managed, how deprecations are communicated, and how changes in webhook schemas are handled. If these practices are weak, you may face ongoing integration drift and repeated maintenance cost.
| Approach | Typical fit | Integration shape | Security scope focus | Operational considerations |
|---|---|---|---|---|
| Hosted checkout / redirect | Teams prioritizing speed to launch | Less embedded logic; fewer client-side responsibilities | Reduces exposure to raw card data handling | Customization limits; rely on vendor UX components |
| Embedded payment fields | Brands needing consistent UX | Client-side components integrated via vendor scripts/APIs | Minimizes stored card data using tokenization patterns | Requires careful front-end implementation and testing |
| API-led payments with tokenization | Platforms with advanced workflows | Deep API usage; more control over transaction states | Token vaulting and structured secure data flows | Higher engineering effort; stronger need for idempotency and webhooks |
| Payment orchestration layer | Merchants optimizing authorization across providers | Routes transactions based on performance signals | Depends on orchestration + underlying processor model | Data and routing governance become critical |
| In-house payment gateway development | Large organizations with specialized requirements | Custom gateway + integrations | Highest burden to meet security and compliance controls | Longer timelines; requires strong security engineering and audit readiness |
It is worth emphasizing that “best approach” depends on your business maturity. Many businesses start with hosted checkout to reduce time-to-launch, then migrate to embedded fields for UX or API-led tokenization for deeper workflows. The key is planning migration with minimal risk. Migration is not purely technical—it affects analytics, reconciliation, support workflows, and risk policies.
Also, orchestration layers can dramatically improve approval rates when properly governed, but they also add complexity. You must understand how orchestration impacts transaction identifiers, event reporting, and fee structures. If the orchestration layer chooses among processors, then different processor behaviors could affect the mapping of statuses and the timing of settlement.
Below is a practical, step-by-step plan you can apply when selecting and deploying Payment Processing Systems. Conditions/requirements are included to help you prevent common rollout failures.
To further reduce rollout risk, many expert teams add two extra layers to this plan: (1) a “data model mapping” exercise and (2) a “runbook and incident rehearsal” exercise.
Data model mapping means explicitly documenting how payment-related entities map between systems: your order system, your payment platform, your CRM (if applicable), your accounting system, and your support tooling. The deliverable is often a table or schema design that lists each field needed for operations (e.g., order ID, payment intent ID, authorization ID, capture ID, refund ID, dispute ID, customer ID) and defines which system is the source of truth.
Runbook rehearsal means practicing common incident scenarios before production traffic is fully enabled. For example:
These rehearsals are time-consuming but can be decisive for business performance. Payments are one of the few systems where operational delays can directly block revenue or create customer dissatisfaction.
Additionally, consider asking for contract language or service commitments that reflect operational reality. Many issues are not caused by the platform’s cryptography; they are caused by misunderstandings about how events are delivered, what happens when endpoints are down, and how vendor support works during outages. If a vendor offers strong operational tooling but cannot support migrations or incident processes, you might choose incorrectly.
For businesses with strict change management requirements, you should also confirm:
To keep this discussion grounded, the security and compliance themes align with widely recognized industry guidance such as PCI DSS documentation and payment ecosystem materials from reputable standards and payment organizations. For business continuity and web security fundamentals, incident and operational top practices are often covered in industry research and provider documentation.
Sources you can consult: PCI Security Standards Council materials on PCI DSS; payment industry operational and security guidance published by major payment ecosystem bodies and widely used compliance frameworks.
They are the combined technologies and workflows that take payment information from a checkout experience, request authorization, capture and settle funds, and provide reporting for reconciliation—while also supporting security, fraud controls, and dispute management.
Very modern designs rely on tokenization and secure data handling patterns to avoid storing raw card data. The exact approach depends on whether you use hosted checkout, embedded payment fields, or API-led tokenization.
Authorization is a confirmation that funds can be reserved for a transaction. Capture is the action that finalizes the charge. Depending on your business model, you may capture immediately or later (e.g., preauthorization for delayed fulfillment).
Declines can result from issuer rules, insufficient funds, mismatched billing details, risk screening thresholds, network issues, or configuration problems in the merchant’s processing setup. A strong system provides clear status handling and actionable reporting.
A balanced posture uses layered risk controls and policy governance. Fraud systems should be tuned to reduce true fraud while minimizing false positives that block legitimate customers. Testing and monitoring approval-rate impact are essential.
Finance teams typically need reliable reconciliation data: consistent transaction identifiers, accurate status mapping (authorized/captured/settled), clear refund linkage to original payments, and usable exports or APIs for settlement reporting.
Not always. In-store often involves terminals and different hardware and settlement patterns, while online relies more heavily on webhooks, payment method modules, and checkout integration. However, the principles—security, lifecycle reliability, and reporting—remain consistent.
Common risks include webhook misconfiguration, mismatched reconciliation logic, inadequate testing of refunds/chargebacks, lack of idempotency in payment retries, and underestimating how different payment methods settle.
Run a PoC using realistic scenarios and request documentation about security architecture, operational support processes, webhook behavior, dispute workflows, and a transparent fee schedule that can be mapped to your historical data.
Establish change management for risk rules and payment configuration, monitor payment success metrics, define ownership for incident response, and keep a rollback plan to prevent prolonged operational disruption.
Payment Processing Systems should be selected with an operational mindset: security architecture, transaction lifecycle reliability, risk governance, and reconciliation accuracy matter as much as checkout conversion. By comparing approaches, validating integration behavior in a proof-of-concept, and meeting the conditions outlined above, businesses can deploy a payment stack that supports steady growth—without creating avoidable operational friction.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans

Explore the Tranquil Bliss of Idyllic Rural Retreats

How to Make Lasting Memories at Disneyland Attractions

Affordable Phones and Plans for Seniors

Affordable Full Mouth Dental Implants Near You

Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!

Discovering Springdale Estates

Unveiling RS Sul Telecom Services

The Guide to Car Trading

Delving into Worldline Issuing
In the evolving realm of digital payments, Worldline Issuing stands at the forefront, providing seamless and secure solutions for card issuance and management. As the payments industry transitions towards more efficient and customer-centric practices, Worldline Issuing offers a comprehensive suite of services tailored to the needs of financial institutions and end-users, enhancing both operational efficiency and security.
Understanding Worldline Issuing Solutions
Dive into the realm of Worldline Issuing, a cornerstone in the fintech landscape that facilitates secure and efficient digital payment solutions. Worldline has established itself as a key player by offering sophisticated tools to streamline financial transactions, thereby enhancing consumer convenience and fostering secure monetary operations worldwide through innovative issuing services.
The Comprehensive Guide to Corpay.com
This article delves into the features and benefits of Corpay.com, a key player in the financial transaction space. Known for its innovative solutions, the website offers robust tools for managing financial transactions, making it a valuable resource for businesses and individuals alike seeking efficiency and reliability in managing their financial operations. Explore its offerings to gain a deeper understanding of its industry impact.
Understanding Lifetime Benefits Solutions and How to Choose Wisely
This guide explains how to evaluate Lifetime Benefits Solutions services with a practical, objective lens. It outlines what the keywords typically refer to in benefits planning, why customers compare providers and pricing structures, and how to approach decisions responsibly. You’ll also find a conditions checklist, a comparison table framework, and a set of FAQs to support informed next steps.
Understanding the Impact of 0009968545
This article explores the significance and implications of the keyword '0009968545' within industry and academia. Although '0009968545' might appear as an abstract sequence of numbers to the unaccustomed eye, it potentially represents an International Standard Book Number (ISBN) that could be a crucial reference for numerous academic publications. This analysis examines the potential contexts and influences of this code, offering insights from an expert's perspective.
Digio Livelo: How It Works and What to Compare
Digio Livelo is top understood by comparing how earning, redemption, and service terms align with your goals. This guide explains the background of points-and-rewards ecosystems, typical partner mechanics, and decision factors such as fees, eligibility, transfer rules, and support quality. It’s an objective overview to help you evaluate fit with care.
